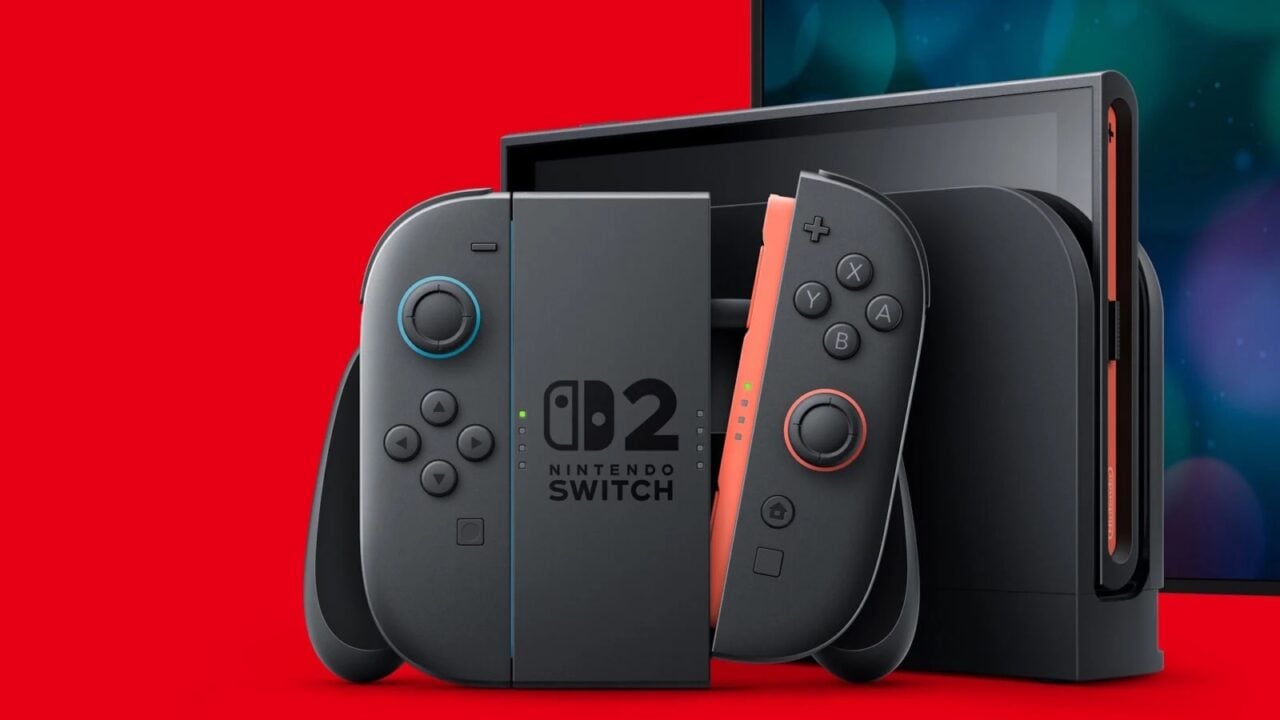
Hackers have officially bypassed Nintendo Switch 2 security protocols in October 2026 to execute below-KIP binary access, directly dumping launch title game files onto personal computers and paving the way for rapid reverse-engineering, custom homebrew firmware, and early console emulation. According to verified reports from Kotaku, security researchers and scene modders successfully expanded on an entry-point exploit originally tied to the delisted SmileBASIC software. This breakthrough grants unauthorized access to lower-level system privileges, enabling enthusiasts to rip decrypted game packages and analyze proprietary operating libraries. While previous exploits required sandboxed execution inside delisted utility software, developers are actively engineering tethered triggers that execute without software dependencies before Nintendo issues mandatory firmware mitigations. As tech infrastructure evolves alongside developments like the [Anthropic IPO: Claude Creator Files SEC Prospectus [Confirmed]](/news/anthropic-ipo-filing-ai-gaming-industry), reverse-engineering teams are adopting automated scripting to disassemble proprietary file formats at record speed. Nintendo engineers are already drafting countermeasure patches to revoke binary execution rights across commercial retail units. However, hardware-level researchers warn that if the vulnerability resides in foundational silicon memory mappings, software revisions might merely slow down persistent exploitation across the initial production run of hardware.